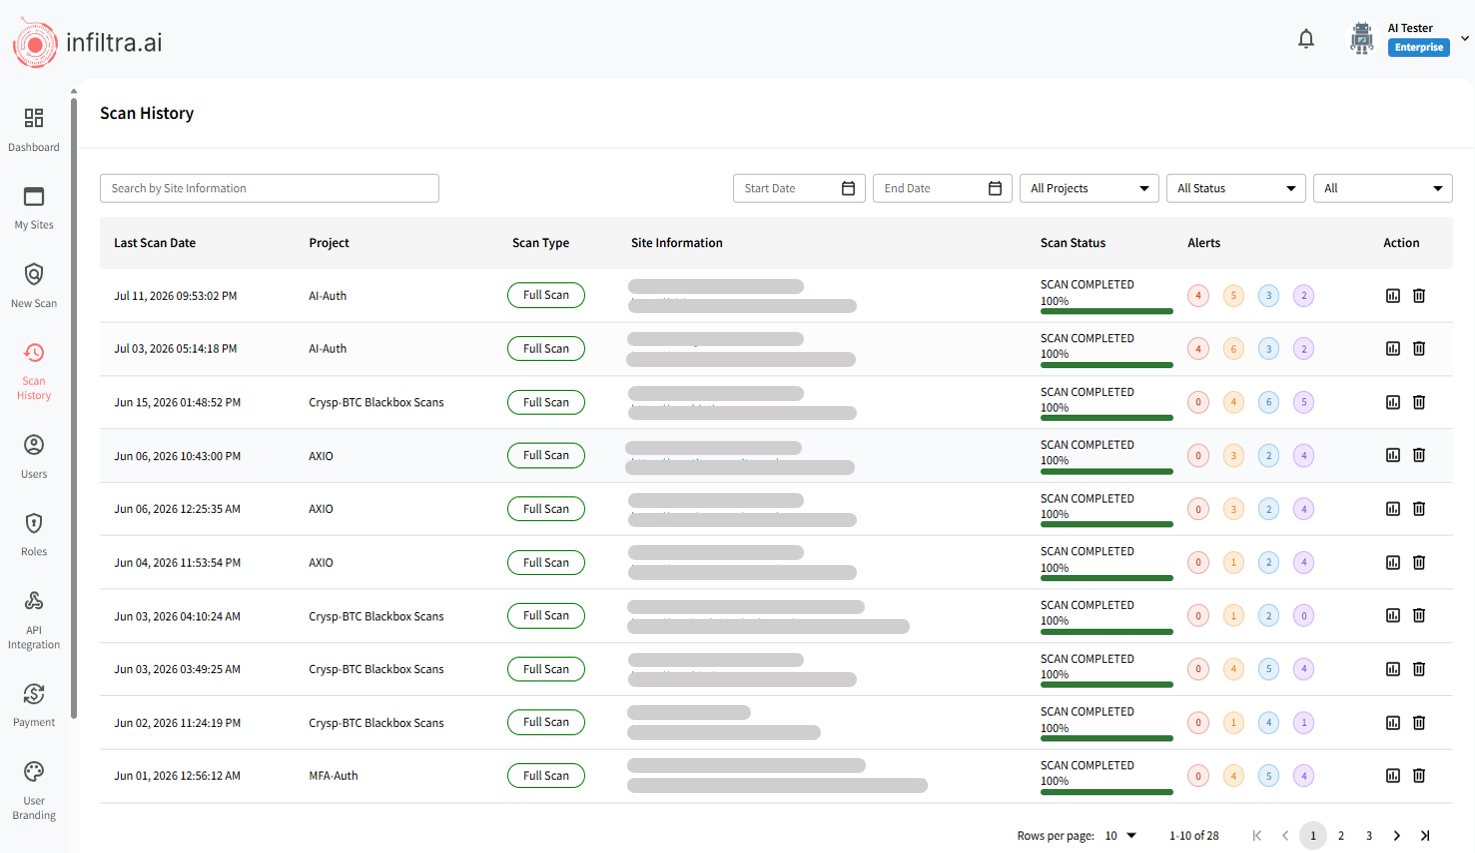
3-Minute Technical Walkthrough: Autonomous Exploitation
Fast-paced overview demonstrating how Infiltra's vision-enabled browser agent and autonomous exploit engine discover attack surfaces and validate findings end-to-end.
Founder-led technical walkthroughs, sanitized executive audit reports, engineering whitepapers, and regional compliance testing guides.
Watch how Infiltra's autonomous AI agents discover attack surfaces, navigate multi-factor auth, execute precision exploits, and generate audit-ready evidence.
Technical deep dives led by our founders covering agentic exploit logic, AI red teaming methodology, and CI/CD automation.
Fast-paced overview demonstrating how Infiltra's vision-enabled browser agent and autonomous exploit engine discover attack surfaces and validate findings end-to-end.
In-depth session stepping through scope onboarding, dual-factor TOTP/OOB authentication setup, multi-step exploitation logic, and verifiable SOC 2 remediation proof.
Adversarial testing across LLMs, prompt injection, RAG data poisoning, and unsafe MCP tool execution in autonomous agent workflows.
See how engineering teams integrate deterministic exploit retesting into GitHub Actions and GitLab pipelines to prevent regressions before releases.
Access our curated library of technical frameworks, deployment guides, and sanitized pentest reports designed to help you evaluate and operationalize agentic pentesting. Whether you are benchmarking autonomous AI validation or transitioning from annual audits to continuous verification, these resources provide the blueprint.
Business Risk Assessment & Remediation Roadmap
See how our agents bridge the gap between security leadership and engineering teams, translating complex vulnerabilities into clear business risks with actionable remediation steps.
Transition from Annual Audits to Daily Autonomous Retesting
A blueprint for high-growth startups and security leaders looking to transition from slow, annual compliance audits to resilient, daily automated verification.
Agentic Exploit Validation vs. Traditional DAST & Scanners
A rigorous comparison of modern AppSec testing models. Explore the trade-offs of legacy DAST, manual testing, and continuous agentic validation workflows.
Practical guides to AI penetration testing and AI red teaming, and to the security testing requirements in the laws and standards that apply where you operate.
How AI penetration testing and AI red teaming work, and how to test LLM applications, AI agents and MCP servers.
How AI agents test web apps and APIs, and how they compare with manual tests and scanners.
Attack techniques, OWASP mapping and a repeatable lifecycle for LLM apps and agents.
What to test in an AI agent, mapped to the OWASP Top 10 for Agentic Applications.
Attacks on MCP servers and agent tools, with an 11-step testing checklist.
Each 2025 risk explained, with real-world exploit scenarios and how to test for it.
Federal and state government requirements, and AI penetration testing for Australian organizations.
Hosting, data residency and Australian regulation for on-demand testing.
ISM-2118 and ISM-2119, Essential Eight scanning, PSPF, CPS 234 and the SOCI rules.
Victoria (VPDSS and health), NSW, Queensland, WA and SA requirements compared.
HIPAA, the FTC Safeguards Rule, NYDFS, FedRAMP and CMMC.
What the HIPAA Security Rule expects today, the proposed annual penetration test and how to build a testing program.
FTC, NYDFS, FedRAMP and CMMC compared
Explicit penetration testing rules in US regulation, from the FTC Safeguards Rule and NYDFS to FedRAMP and CMMC.
The GDPR, NIS2, DORA and the EU AI Act.
How penetration testing meets the GDPR requirement to regularly test, assess and evaluate your security measures.
Article 21, yearly testing and TLPT
What NIS2 and DORA expect from security testing, including DORA's threat-led penetration testing.
Testing, robustness and adversarial testing requirements in the EU AI Act, with the updated 2027 and 2028 deadlines.
The DPDP Act and Rules, and VAPT requirements from CERT-In, the RBI and SEBI.
What India's DPDP Act and Rules require for security safeguards and breach reporting, and how testing helps you prepare.
VAPT and audit requirements from CERT-In, the RBI and SEBI, with timelines for testing, reporting and fixes.
PCI DSS, SOC 2 and ISO 27001, which apply across regions.
Requirement 11.4 explained: frequency, methodology, segmentation and retesting.
What SOC 2 and ISO 27001 auditors expect, and how to keep evidence current.
Ready to see deterministic exploit validation on your application?
Book a demo to see AI penetration testing and AI red teaming on your own applications.