Web App
"Customer signs in & opens support chat to request a refund."
- Auth & session hijacking vulnerabilities
Deploy autonomous AI security agents that think like attackers to uncover and validate vulnerabilities before adversaries do.
Continuous penetration testing for Web Applications & APIs, combined with adversarial red teaming for LLM apps, RAG pipelines, and agentic workflows—delivering verified proof of exploitability with zero blind spots.
Web applications, REST endpoints, auth logic, and external cloud perimeters.
Explore Web Pentesting →Prompt injections, RAG retrieval leaks, autonomous reasoning loops, and connected MCP tools.
Explore AI Red Teaming →Modern AI applications are complex multi-tier systems. A prompt doesn't just touch the LLM—it traverses your web login, backend APIs, LLM guardrails, RAG context, autonomous agent reasoning, and connected MCP tools.
Autonomous AI agents and continuous deployments create attack surfaces that annual tests and static scanners miss.
Prompts, models, RAG context, and tool definitions change weekly. Annual point-in-time assessments leave critical security gaps.
Agents read databases, invoke backend APIs, and trigger payments. A compromised model can execute unauthorized actions with full privileges.
Indirect prompt injection, RAG context poisoning, and MCP tool hijacking require multi-step reasoning that traditional DAST tools cannot simulate.
Enterprise buyers, board audits, and regulations (EU AI Act, OWASP GenAI) require verified proof-of-exploit rather than speculative alert noise.
Autonomous testing adapted to the unique architecture of each attack surface.
Set target URLs, authenticate multi-role sessions (with MFA automation), define test scope and region. Import OpenAPI/Postman specs where available.
Autonomous browser agents crawl authenticated paths, map stateful business workflows, endpoints, hidden parameter dependencies, and RBAC matrices.
Agents attempt active exploitation across business logic, multi-step privilege escalation, BOLA/IDOR object flaws, and parameter tampering to validate real impact.
Receive zero-noise findings with step-by-step reproduction payloads and remediation code. Automatically retest fixed endpoints on demand.
Connect your LLM application, chatbot endpoint, or autonomous agent. Select red-team risk profiles mapped to OWASP GenAI & Agentic standards.
Identify prompt ingestion channels, system prompts, guardrails, vector RAG knowledge sources, and external tools/MCP server integrations.
Specialized red-team agents dynamically adapt jailbreak techniques, indirect prompt injections, RAG poisoning, and agent goal hijacking.
Get verifiable exploit traces, bypassed guardrail logs, and remediation guidance. Re-run continuous regression scans after every model or prompt update.
Application security now has to keep pace with continuous software delivery and rapidly evolving LLM applications and AI agents.
Legacy automated tools identify patterns and known issues, but they rarely reason through workflows, validate real impact or adapt attacks to context.
Code, APIs, prompts, models, RAG sources and tools keep changing after an assessment, and manual scheduling cannot keep pace with CI/CD or AI iteration cycles.
Experienced penetration testers and AI security specialists are difficult and expensive to apply continuously across every application and material change.
Every fix needs validation. AI systems also benefit from regression testing after material model, prompt, RAG, tool or agent workflow changes.
Three core pillars designed for modern software delivery and autonomous AI systems.
Move beyond shallow endpoint fuzzing. Specialized agents authenticate, reason through complex business state, and validate exploit impact.
Chains interdependent API calls and browser actions across session states to uncover deep logic vulnerabilities.
Manipulates multi-user parameters, skips workflow steps, and probes object-level authorization across tenant boundaries.
Maintains persistent session state with browser-driven login automation, OAuth/JWT support, and TOTP MFA flows.
Automated adversarial evaluation across chatbots, guardrails, vector RAG pipelines, MCP tools, and autonomous AI agents.
Adversarial attacks test for direct jailbreaks, multi-turn system prompt extraction, and safety guardrail subversion.
Injects adversarial context into retrieval pipelines to validate vector boundary separation and sensitive data isolation.
Tests autonomous agents for plan manipulation, unauthorized tool execution, and MCP server privilege abuse.
Replace speculative scan warnings with verified proof-of-exploit evidence and instant delta retesting after fixes.
Every finding includes exact request/response traces, reproduction scripts, and clear remediation guidance.
Re-verify individual endpoints or AI systems on demand after code, prompt, model, or tool configuration updates.
Ephemeral isolated assessment runners, Sydney/US/EU data residency options, CI/CD webhooks, and GRC exports.
A unified workflow for assessment activity, validated findings, remediation progress and retesting across Web Apps, APIs, LLM Applications and AI Agents.
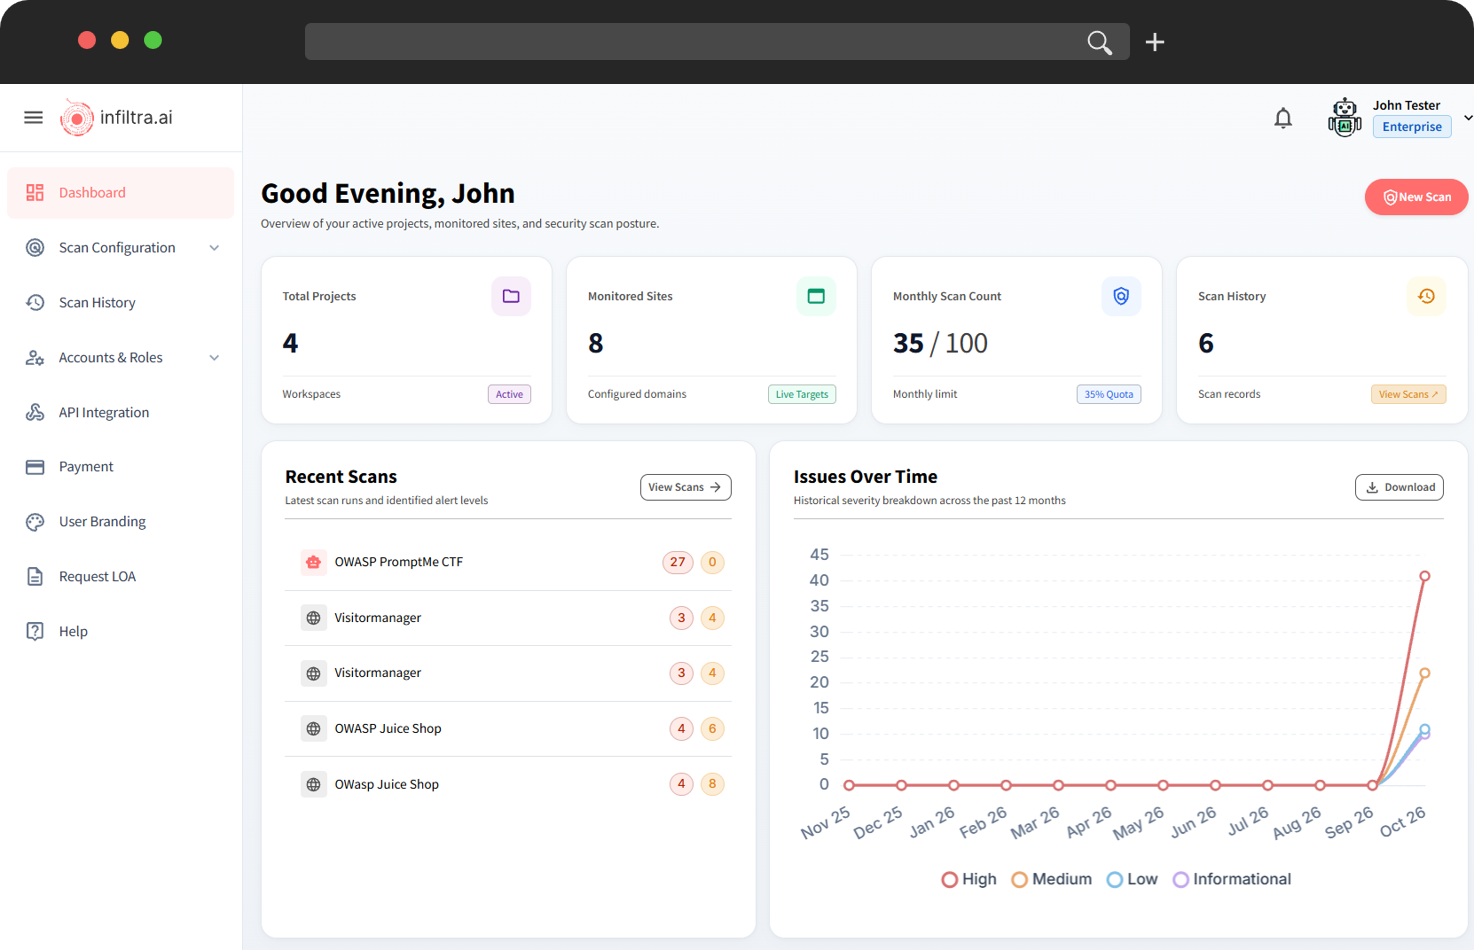
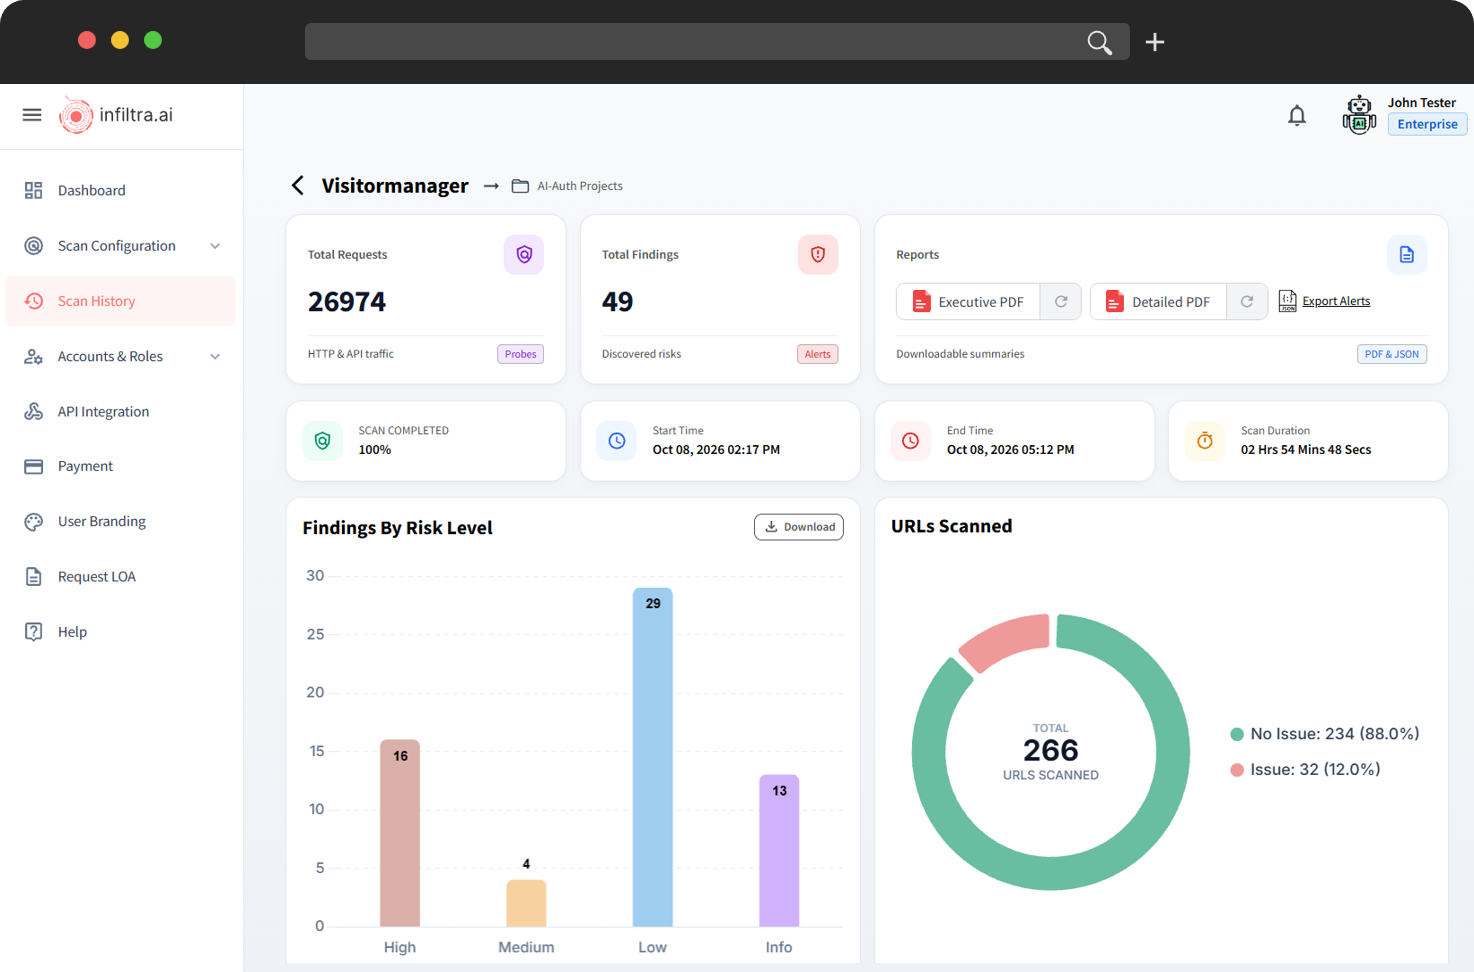
Teams use Infiltra to move from infrequent manual security checks to continuous, on-demand assurance.
 Quantumcorp
“Infiltra.ai has become an indispensable security extension to our app team. Instead of waiting months for third-party penetration test reports, we get validated proof-of-exploit findings and instant retesting that keep us ahead of emerging threats.”
 Modern Innovations
“Infiltra.ai provides continuous, automated testing at a price point a fast-growing startup can actually afford. The zero-noise reports and clear reproduction payloads have saved our engineering team dozens of triage hours every sprint.”
Enterprise-grade architectural isolation, global data residency options, and active production-safety guardrails designed for high-assurance autonomous testing.
Each scan executes inside a dedicated compute container running a single assessment at a time. Upon completion, the container state is fully reset and restarted for every new scan—ensuring no prompts, attack states, or runtime data are retained.
Primary tenant data is anchored in AWS Australia Region (Sydney), with dedicated US and EU residency options selectable per assessment. All session tokens, traces, and reports are protected by AES-256 and TLS 1.3.
Safely test live production environments with user-controlled RPS throttling, strict scope boundaries, and instant emergency scan termination. In parallel, built-in Agent guardrails prevent autonomous testing from going out of bounds and causing performance degradation on tested systems.
Infiltra was born from a recurring problem: point-in-time security testing goes stale. We built an autonomous platform for continuous, evidence-driven application security and are extending the same approach to the emerging risks in LLM Applications and AI Agents.
Leading engineering innovation, distributed systems architecture, and autonomous offensive AI testing engines.
Specializing in enterprise cybersecurity advisory, offensive security assessments, and risk remediation programs.
Driving cybersecurity strategy, cloud resilience, and continuous product evolution for mission-critical applications.
Autonomous penetration testing for modern web apps & APIs, paired with adversarial red teaming for LLMs, RAG pipelines, and autonomous agents. Uncover exploitable flaws before attackers do—with verified proof of closure.
Comprehensive reconnaissance and offensive stress testing before web features or AI prompts deploy to production.
Instantly re-run exploit payloads to mathematically verify developer fixes without waiting for manual re-pentests.
Detect vulnerabilities immediately when prompts drift, new MCP tools/APIs are exposed, or model weights change.
Verifiable proof logs, reproducible payloads, and executive compliance reports aligned to OWASP Top 10.